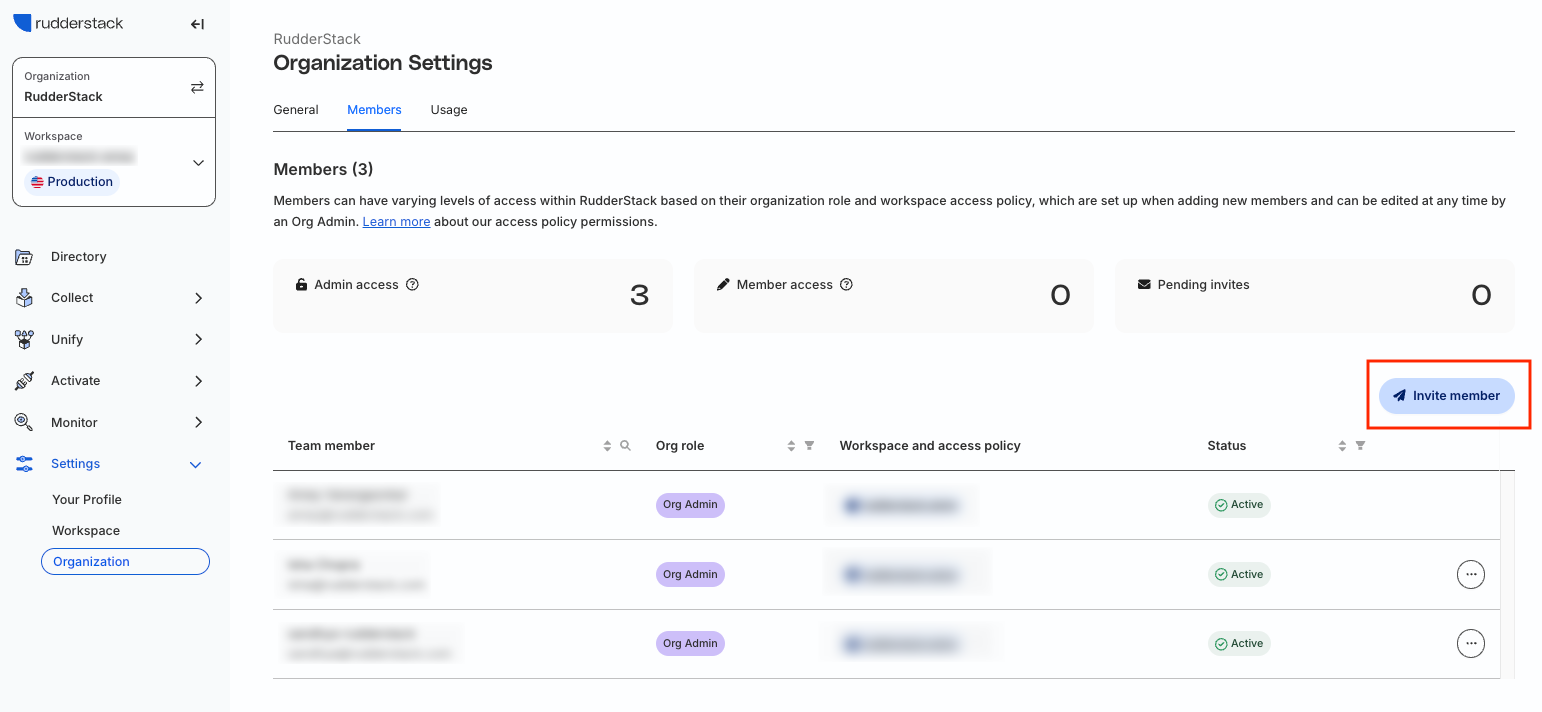
We now offer more granular user access controls across the RudderStack web app. We have created two roles: Org Admin, and Org Member. Org Member roles can be further customized with resource roles, e.g. Transformations Admin to provide granular access policies.
Prior to this release, our user roles consisted of Admin, Read-write, and Read-only, and gave broad access across all features throughout the RudderStack app. With this release, you can define granular access roles for teams that require more specific access policies.
For example, a user might be responsible for writing JavaScript transformations, but should not have access to controlling data pipelines. This user can be given the Transformations Admin role, but will not be able to create, edit, or delete a source or destination.
Users are invited at the organization level and access policies are set during the invite process. Individual access policies can then be managed in Organization Settings in the RudderStack dashboard under the Members tab.
Start by navigating to the Members tab in Organization Settings. This will give you a view of all the users in the organization, their roles, and their granular access policies.
See the User Management guide to get started.