# Amazon S3 Destination

<p><a href="https://aws.amazon.com/s3/" >Amazon S3</a> (Simple Storage Service) is a cloud-based object storage service that lets customers and businesses store their data securely and at scale.</p>
<p>Find the open source transformer code for this destination in the <a href="https://github.com/rudderlabs/rudder-transformer/tree/main/src/v0/destinations/s3" >GitHub repository</a>.</p>
<!-- end-chunk -->
<!-- begin-chunk -->
<h2 id="prerequisites">Prerequisites</h2><ul>
<li>Make sure to <a href="#s3-bucket-setup" >set up your S3 bucket</a> with the required <a href="#permissions" >permissions</a>.</li>
</ul>
<!-- end-chunk -->
<!-- begin-chunk -->
<h2 id="setup">Setup</h2><ol>
<li>From your <a href="https://app.rudderstack.com/" >RudderStack dashboard</a>, add a source. Then, from the list of destinations, select <strong>Amazon S3</strong>.</li>
<li>Assign a name to the destination and click <strong>Continue</strong>.</li>
</ol>
<!-- end-chunk -->
<!-- begin-chunk -->
<h3 id="connection-settings">Connection settings</h3>
<blockquote class="success">
  <div class="tip-quote">
    
    <div class="tip-text">
      If you have already configured the AWS credentials in your RudderStack setup via <a href="https://docs.aws.amazon.com/sdk-for-go/v1/developer-guide/configuring-sdk.html#specifying-credentials" >environment credentials</a> or by following the steps in the <a href="#option-3-allow-rudderstack-to-write-into-bucket" >Permissions setup</a> section, then specifying only <strong>S3 Bucket Name</strong> and <strong>Prefix</strong> (optional but recommended) is sufficient to set up your S3 destination.
    </div>
  </div>
</blockquote>
<table>
  <thead>
      <tr>
          <th>Setting</th>
          <th>Description</th>
      </tr>
  </thead>
  <tbody>
      <tr>
          <td>S3 Bucket Name</td>
          <td>Enter your S3 bucket name.</td>
      </tr>
      <tr>
          <td>Prefix</td>
          <td>If specified, RudderStack creates a folder in the S3 bucket with this name and pushes all data within that folder. For example, <code>s3://&lt;bucket_name&gt;/&lt;prefix&gt;/</code>.</td>
      </tr>
      <tr>
          <td>Role-based Authentication</td>
          <td>This setting is toggled on by default and lets you use the <a href="https://www.rudderstack.com/docs/destinations/aws-iam-role-for-rudderstack/" >RudderStack IAM role</a> for authentication.</td>
      </tr>
      <tr>
          <td>IAM Role ARN</td>
          <td>This setting is visible if <strong>Role-based Authentication</strong> is toggled on. Enter the ARN of the IAM role in this field.</td>
      </tr>
      <tr>
          <td>Enable Server Side Encryption</td>
          <td>When you enable this setting, RudderStack adds a header <code>x-amz-server-side-encryption</code> with the value <code>AES256</code> to the <code>PutObject</code> request when sending the data to the S3 bucket. <br /><br />See <a href="#s3-managed-keys" >Encryption with S3 managed keys</a> for more information.</td>
      </tr>
  </tbody>
</table>
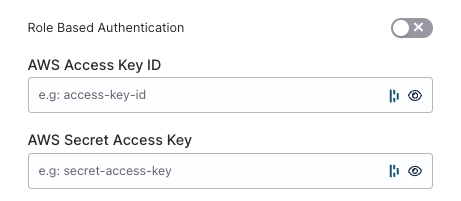
<p>You will see the following settings if <strong>Role-based Authentication</strong> is toggled off:</p>
<table>
  <thead>
      <tr>
          <th>Setting</th>
          <th>Description</th>
      </tr>
  </thead>
  <tbody>
      <tr>
          <td>AWS Access Key ID</td>
          <td>Enter the AWS access key ID to authorize RudderStack to write to your S3 bucket.</td>
      </tr>
      <tr>
          <td>AWS Secret Access Key</td>
          <td>Enter the secret access key corresponding to the Access Key ID.</td>
      </tr>
  </tbody>
</table>
<p>See the <a href="#option-2-create-iam-user-and-provide-credentials" >Permissions</a> section more information on obtaining the <strong>AWS Access Key ID</strong> and <strong>AWS Secret Access Key</strong> values.</p>

<html lang="en">
<blockquote class="info">
  <div class="tip-quote">
    
    <div class="tip-text"><p>Note the following:</p>
<ul>
<li>RudderStack recommends using <strong>Role-based Authentication</strong> as the access keys-based authentication method is deprecated and will be discontinued soon.</li>
<li>In both the role-based and access key-based authentication methods, you need to set a policy specifying the required <a href="#permissions" >permissions</a> for RudderStack to write to your S3 bucket.</li>
<li>If you are using your S3 bucket as an intermediary object storage for sending events to a <a href="https://www.rudderstack.com/docs/destinations/warehouse-destinations/" >warehouse destination</a>, then see the <a href="#s3-permissions-for-warehouse-destinations" >S3 permissions for warehouse destinations</a>.</li>
</ul></div>
  </div>
</blockquote>

</html>
<!-- end-chunk -->
<!-- begin-chunk -->
<h4 id="consent-management-settings">Consent management settings</h4><table>
  <thead>
      <tr>
          <th>Setting</th>
          <th>Description</th>
      </tr>
  </thead>
  <tbody>
      <tr>
          <td>Consent management settings</td>
          <td>Configure the consent management settings for the specified source by choosing the <strong>Consent management provider</strong> from the dropdown and entering the relevant consent category IDs. <br /><br />See <a href="https://www.rudderstack.com/docs/data-governance/consent-management/overview/" >Consent Management in RudderStack</a> for more information on this feature.</td>
      </tr>
  </tbody>
</table>
<!-- end-chunk -->
<!-- begin-chunk -->
<h2 id="s3-bucket-setup">S3 bucket setup</h2><ol>
<li>Go to your <a href="https://s3.console.aws.amazon.com/s3/" >S3 Management console</a>.</li>
<li><a href="https://docs.aws.amazon.com/AmazonS3/latest/userguide/creating-bucket.html" >Create a new bucket</a>. Alternatively, you can choose an existing bucket.</li>
</ol>

<html lang="en">
<blockquote class="info">
  <div class="tip-quote">
    
    <div class="tip-text">It is recommended to create a new bucket for storing events coming from RudderStack.</div>
  </div>
</blockquote>

</html>
<!-- end-chunk -->
<!-- begin-chunk -->
<h3 id="permissions">Permissions</h3><p>To send events to S3 successfully, you need to give RudderStack the necessary permissions to write to your bucket. You can choose any of the following approaches based on your company&rsquo;s security policies and setup preferences:</p>
<!-- end-chunk -->
<!-- begin-chunk -->
<h4 id="option-1-use-rudderstack-iam-role">Option 1: Use RudderStack IAM role</h4>
<blockquote class="success">
  <div class="tip-quote">
    
    <div class="tip-text">
      It is highly recommended to use this option for setting up the required S3 bucket permissions.
    </div>
  </div>
</blockquote>
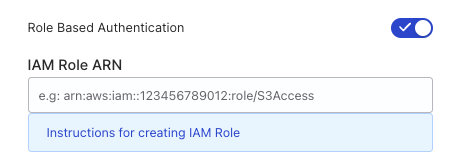
<p>Use this approach if you are going to set up the S3 destination in RudderStack using <strong>Role Based Authentication</strong>.</p>

<figure class="image--main "  >
    <a 
         href="/docs/images/event-stream-destinations/role-based-authentication.webp"
        
        >
        <img src="/docs/images/event-stream-destinations/role-based-authentication.webp" 
         alt="Role based authentication"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

<ol>
<li><a href="https://www.rudderstack.com/docs/destinations/aws-iam-role-for-rudderstack/" >Create a RudderStack IAM role</a>.</li>
<li>Use the following S3 permissions policy for creating the role:</li>
</ol>
<div class="rs-code">
  <div class="rs-code__head">json<button class="rs-code__copy" type="button">
      
      Copy
    </button>
  </div>
  <div class="highlight"><pre class="chroma"><code class="language-json" data-lang="json">{
  &#34;Version&#34;: &#34;2012-10-17&#34;,
  &#34;Statement&#34;: [
    {
      &#34;Effect&#34;: &#34;Allow&#34;,
      &#34;Action&#34;: &#34;s3:PutObject&#34;,
      &#34;Resource&#34;: &#34;arn:aws:s3:::&lt;S3_BUCKET_NAME&gt;/*&#34;
    }
  ]
}</code></pre></div>
</div>
<p>Make sure to replace <code>&lt;S3_BUCKET_NAME&gt;</code> with the actual bucket name.</p>
<ol start="3">
<li>After creating the role, note and specify the <strong>IAM Role ARN</strong> to set up your S3 destination.</li>
</ol>
<!-- end-chunk -->
<!-- begin-chunk -->
<h4 id="option-2-create-iam-user-and-provide-credentials">Option 2: Create IAM user and provide credentials</h4>
<blockquote class="danger">
    <div class="tip-quote">
        
        <div class="tip-text"><p>Note that:</p>
<ul>
<li>Using <a href="#option-1-use-rudderstack-iam-role" ><strong>Role-based Authentication (Option 1)</strong></a> is highly recommended as this method is now deprecated and will be discontinued soon.</li>
<li>AWS <strong>does not</strong> recommend access key credentials-based authentication.</li>
</ul></div>
    </div>
</blockquote>
<p>Use this approach to set up the S3 destination in RudderStack using <strong>Access Key Based Authentication</strong>.</p>

<figure class="image--main "  >
    <a 
         href="/docs/images/event-stream-destinations/access-key-based-authentication.webp"
        
        >
        <img src="/docs/images/event-stream-destinations/access-key-based-authentication.webp" 
         alt="Access key based authentication"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

<html lang="en">
<blockquote class="info">
  <div class="tip-quote">
    
    <div class="tip-text">If the AWS credentials are already configured on your instance (see <a href="#option-4-self-hosted-rudderstack" >Option 4</a>) where the RudderStack server is set up, you do not need to specify these credentials.</div>
  </div>
</blockquote>

</html>
<ol>
<li>Log in to your <a href="https://console.aws.amazon.com/iam/" >Amazon AWS IAM Console</a>.</li>
<li><a href="https://docs.aws.amazon.com/IAM/latest/UserGuide/id_users_create.html" >Create an IAM user</a>. Choose a policy that has <strong>write</strong> access to your bucket. Alternatively, you can <a href="https://docs.aws.amazon.com/IAM/latest/UserGuide/access_policies_create-console.html#access_policies_create-start" >create a new policy</a> with the following permissions and attach it to the IAM user:</li>
</ol>
<div class="rs-code">
  <div class="rs-code__head">json<button class="rs-code__copy" type="button">
      
      Copy
    </button>
  </div>
  <div class="highlight"><pre class="chroma"><code class="language-json" data-lang="json">{
  &#34;Version&#34;: &#34;2012-10-17&#34;,
  &#34;Statement&#34;: [
    {
      &#34;Effect&#34;: &#34;Allow&#34;,
      &#34;Action&#34;: &#34;s3:PutObject&#34;,
      &#34;Resource&#34;: &#34;arn:aws:s3:::&lt;S3_BUCKET_NAME&gt;/*&#34;
    }
  ]
}</code></pre></div>
</div>
<p>Make sure to replace <code>&lt;S3_BUCKET_NAME&gt;</code> with the actual bucket name.</p>
<ol start="3">
<li>Return to the IAM dashboard and go to <strong>Users</strong> under <strong>Access management</strong>. Then, click on the newly-created user.</li>
<li>Go to the <strong>Security credentials</strong> tab and scroll down to <strong>Access keys</strong>.</li>
<li>Click <strong>Create access key</strong>, select the use case as per your requirement, and click <strong>Next</strong>.</li>
<li>If required, set the <strong>Description tag value</strong>, and click <strong>Create access key</strong>.</li>
<li>Note and secure the <strong>Access key</strong> and <strong>Secret access key</strong>. Use these credentials to set up your S3 destination in RudderStack.</li>
</ol>
<!-- end-chunk -->
<!-- begin-chunk -->
<h4 id="option-3-self-hosted-rudderstack">Option 3: Self-hosted RudderStack</h4>
<blockquote class="warning">
  <div class="tip-quote">
    
    <div class="tip-text">Use this approach <strong>only if</strong> you are hosting RudderStack in your own instance and don&rsquo;t want to follow the above options.</div>
  </div>
</blockquote>
<ol>
<li><a href="https://docs.aws.amazon.com/IAM/latest/UserGuide/id_users_create.html" >Create a new IAM user</a> and attach the below policy:</li>
</ol>
<div class="rs-code">
  <div class="rs-code__head">json<button class="rs-code__copy" type="button">
      
      Copy
    </button>
  </div>
  <div class="highlight"><pre class="chroma"><code class="language-json" data-lang="json">{
  &#34;Version&#34;: &#34;2012-10-17&#34;,
  &#34;Statement&#34;: [
    {
      &#34;Effect&#34;: &#34;Allow&#34;,
      &#34;Action&#34;: &#34;*&#34;,
      &#34;Resource&#34;: &#34;arn:aws:s3:::*&#34;
    }
  ]
}</code></pre></div>
</div>
<ol start="2">
<li>Add the following policy to your bucket. Replace <code>ACCOUNT_ID</code>, <code>USER_ARN</code>, and <code>&lt;S3_BUCKET_NAME&gt;</code> with the AWS account ID, user ARN, and the S3 bucket name.</li>
</ol>
<div class="rs-code">
  <div class="rs-code__head">json<button class="rs-code__copy" type="button">
      
      Copy
    </button>
  </div>
  <div class="highlight"><pre class="chroma"><code class="language-json" data-lang="json">{
  &#34;Version&#34;: &#34;2012-10-17&#34;,
  &#34;Statement&#34;: [
    {
      &#34;Effect&#34;: &#34;Allow&#34;,
      &#34;Principal&#34;: {
        &#34;AWS&#34;: &#34;arn:aws:iam::ACCOUNT_ID:user/USER_ARN&#34;
      },
      &#34;Action&#34;: [&#34;s3:PutObject&#34;, &#34;s3:PutObjectAcl&#34;],
      &#34;Resource&#34;: [&#34;arn:aws:s3:::&lt;S3_BUCKET_NAME&gt;/*&#34;]
    }
  ]
}</code></pre></div>
</div>

<html lang="en">
<blockquote class="info">
  <div class="tip-quote">
    
    <div class="tip-text">If you&rsquo;re using the S3 bucket as an <strong>intermediary object storage</strong> for a <a href="https://www.rudderstack.com/docs/destinations/warehouse-destinations/" >warehouse destination</a>, then see <a href="#s3-permissions-for-warehouse-destinations" >S3 permissions for warehouse destinations</a> for more information on the required bucket policy.</div>
  </div>
</blockquote>

</html>
<ol start="3">
<li>Return to the IAM dashboard and go to <strong>Users</strong> under <strong>Access management</strong>. Then, click on the newly-created user.</li>
<li>Go to the <strong>Security credentials</strong> tab and scroll down to <strong>Access keys</strong>.</li>
<li>Click <strong>Create access key</strong>, select the use case as per your requirement, and click <strong>Next</strong>.</li>
<li>If required, set the <strong>Description tag value</strong>, and click <strong>Create access key</strong>.</li>
<li>Note and secure the <strong>Access key</strong> and <strong>Secret access key</strong>.</li>
<li>Add the above credentials to your RudderStack setup environment:</li>
</ol>
<div class="rs-code">
  <div class="rs-code__head">markup<button class="rs-code__copy" type="button">
      
      Copy
    </button>
  </div>
  <pre><code class="language-markup" data-lang="markup">RUDDER_AWS_S3_COPY_USER_ACCESS_KEY_ID=&lt;access_key_id&gt;
RUDDER_AWS_S3_COPY_USER_ACCESS_KEY=&lt;secret_access_key&gt;</code></pre>
</div>
<!-- end-chunk -->
<!-- begin-chunk -->
<h3 id="s3-permissions-for-warehouse-destinations">S3 permissions for warehouse destinations</h3><p>If you&rsquo;re using your S3 bucket as an <strong>intermediary object storage</strong> for a <a href="https://www.rudderstack.com/docs/destinations/warehouse-destinations/" >warehouse destination</a>, then attach the below permissions policy depending on your use case:</p>

<blockquote class="warning">
  <div class="tip-quote">
    
    <div class="tip-text"><p>Note that the below policy is applicable only for the below authentication options:</p>
<ul>
<li><a href="#option-1-use-rudderstack-iam-role" >Using the RudderStack IAM role (recommended)</a></li>
<li><a href="#option-2-create-iam-user-and-provide-credentials" >Using the access key credentials</a></li>
</ul></div>
  </div>
</blockquote>
<div class="rs-code">
  <div class="rs-code__head">json<button class="rs-code__copy" type="button">
      
      Copy
    </button>
  </div>
  <div class="highlight"><pre class="chroma"><code class="language-json" data-lang="json">{
  &#34;Version&#34;: &#34;2012-10-17&#34;,
  &#34;Statement&#34;: [{
    &#34;Effect&#34;: &#34;Allow&#34;,
    &#34;Action&#34;: [
      &#34;s3:GetObject&#34;,
      &#34;s3:PutObject&#34;,
      &#34;s3:PutObjectAcl&#34;,
      &#34;s3:ListBucket&#34;
    ],
    &#34;Resource&#34;: &#34;arn:aws:s3:::&lt;S3_BUCKET_NAME&gt;/*&#34;
  }]
}</code></pre></div>
</div>
<p>For self-hosted RudderStack <a href="#option-3-self-hosted-rudderstack" >(Option 3)</a>, use the following bucket policy in Step 2:</p>
<div class="rs-code">
  <div class="rs-code__head">json<button class="rs-code__copy" type="button">
      
      Copy
    </button>
  </div>
  <div class="highlight"><pre class="chroma"><code class="language-json" data-lang="json">{
  &#34;Version&#34;: &#34;2012-10-17&#34;,
  &#34;Statement&#34;: [{
    &#34;Effect&#34;: &#34;Allow&#34;,
    &#34;Principal&#34;: {
      &#34;AWS&#34;: &#34;arn:aws:iam::ACCOUNT_ID:user/USER_ARN&#34;
    },
    &#34;Action&#34;: [
      &#34;s3:GetObject&#34;,
      &#34;s3:PutObject&#34;,
      &#34;s3:PutObjectAcl&#34;,
      &#34;s3:ListBucket&#34;
    ],
    &#34;Resource&#34;: [&#34;arn:aws:s3:::&lt;S3_BUCKET_NAME&gt;/*&#34;]
  }]
}</code></pre></div>
</div>
<p>Make sure to replace <code>&lt;S3_BUCKET_NAME&gt;</code> with the actual bucket name.</p>
<!-- end-chunk -->
<!-- begin-chunk -->
<h2 id="encryption">Encryption</h2><p>Amazon S3 provides encryption at rest. The objects get encrypted while saving them to the bucket and are decrypted before downloading from S3.</p>
<p>S3 lets you <a href="#set-default-encryption" >set the default encryption behavior for a bucket</a>. It encrypts the objects using server-side encryption with either <strong>Amazon S3 managed keys (SSE-S3)</strong> or <strong>AWS KMS-managed keys (SSE-KMS)</strong>.</p>
<!-- end-chunk -->
<!-- begin-chunk -->
<h4 id="set-default-encryption">Set default encryption</h4><ol>
<li>Log in to your <a href="https://s3.console.aws.amazon.com/s3/" >S3 Management console</a> and select your bucket.</li>
<li>Go to the <strong>Properties</strong> tab and scroll down to <strong>Default encryption</strong>. Then, click <strong>Edit</strong>.</li>
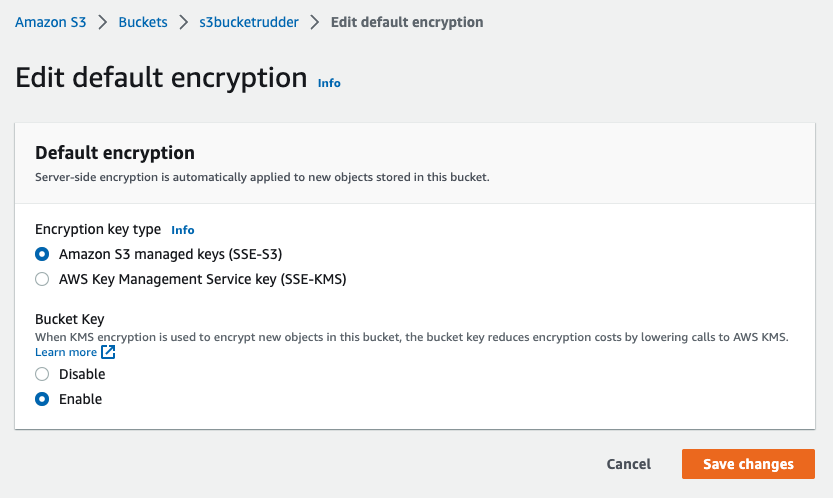
<li>Under <strong>Encryption key type</strong>, choose from <strong>Amazon S3 managed keys (SSE-S3)</strong> or <strong>AWS KMS-managed keys (SSE-KMS)</strong>:</li>
</ol>

<figure class="image--main "  >
    <a 
         href="/docs/images/event-stream-destinations/s3-default-encryption-new.webp"
        
        >
        <img src="/docs/images/event-stream-destinations/s3-default-encryption-new.webp" 
         alt="S3 default encryption"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

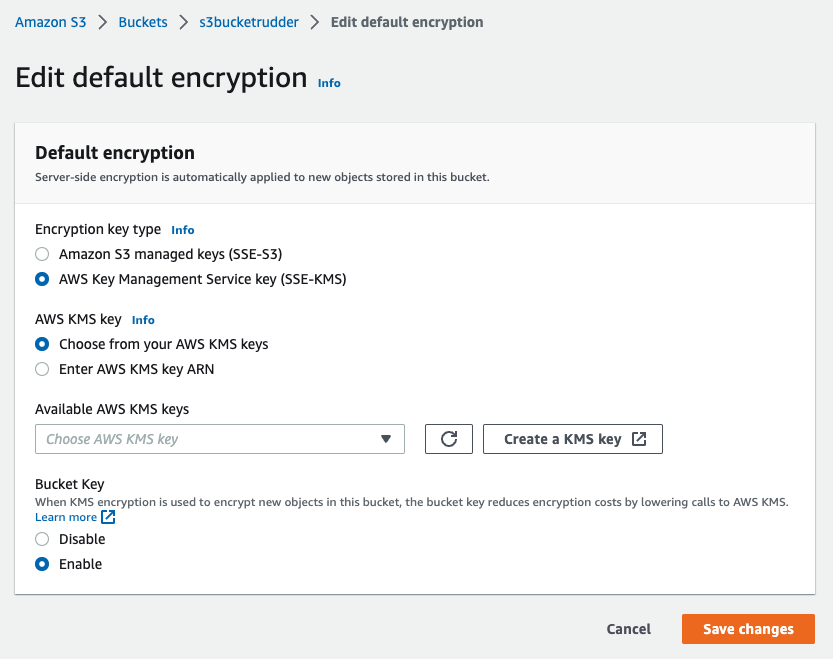
<p>The following settings are applicable if you choose <strong>AWS KMS-managed keys (SSE-KMS)</strong> as the encryption key type:</p>

<figure class="image--main "  >
    <a 
         href="/docs/images/event-stream-destinations/s3-default-encryption-kms.webp"
        
        >
        <img src="/docs/images/event-stream-destinations/s3-default-encryption-kms.webp" 
         alt="KMS encryption configuration"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

<html lang="en">
<blockquote class="info">
  <div class="tip-quote">
    
    <div class="tip-text">You can choose an existing AWS KMS key, enter the ARN of an AWS KMS key, or <a href="#create-a-new-customer-managed-key" >create a new KMS key</a>.</div>
  </div>
</blockquote>

</html>
<ol start="4">
<li>Under <strong>Bucket Key</strong>, choose <strong>Enable</strong> and click <strong>Save changes</strong>.</li>
</ol>
<p>For more information on setting the default encryption behavior for a bucket, see the <a href="https://docs.aws.amazon.com/AmazonS3/latest/userguide/default-bucket-encryption.html" >S3 documentation</a>.</p>
<!-- end-chunk -->
<!-- begin-chunk -->
<h3 id="aws-kms-keys">AWS KMS keys</h3><p>When the <a href="#set-default-encryption" >default encryption</a> is set to <strong>AWS KMS-managed keys (SSE-KMS)</strong>, S3 encrypts the objects using the customer managed keys (CMK) when they are uploaded to the bucket.</p>
<!-- end-chunk -->
<!-- begin-chunk -->
<h4 id="create-a-new-customer-managed-key">Create a new customer managed key</h4><ol>
<li>Log in to the <a href="https://aws.amazon.com/kms/" >AWS Key Management Service (KMS) console</a>.</li>
</ol>

<figure class="image--main "  >
    <a 
         href="/docs/images/event-stream-destinations/aws-kms-1.webp"
        
        >
        <img src="/docs/images/event-stream-destinations/aws-kms-1.webp" 
         alt="KMS console login"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

<ol start="2">
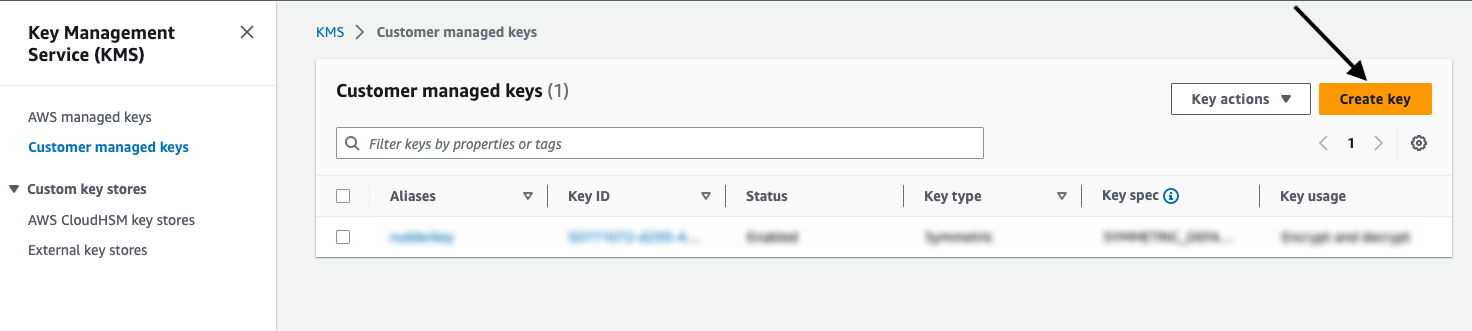
<li>From the left sidebar, go to <strong>Customer managed keys</strong> and click <strong>Create key</strong>.</li>
</ol>

<figure class="image--main "  >
    <a 
         href="/docs/images/event-stream-destinations/aws-kms-2.webp"
        
        >
        <img src="/docs/images/event-stream-destinations/aws-kms-2.webp" 
         alt="Create new CMK"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

<ol start="3">
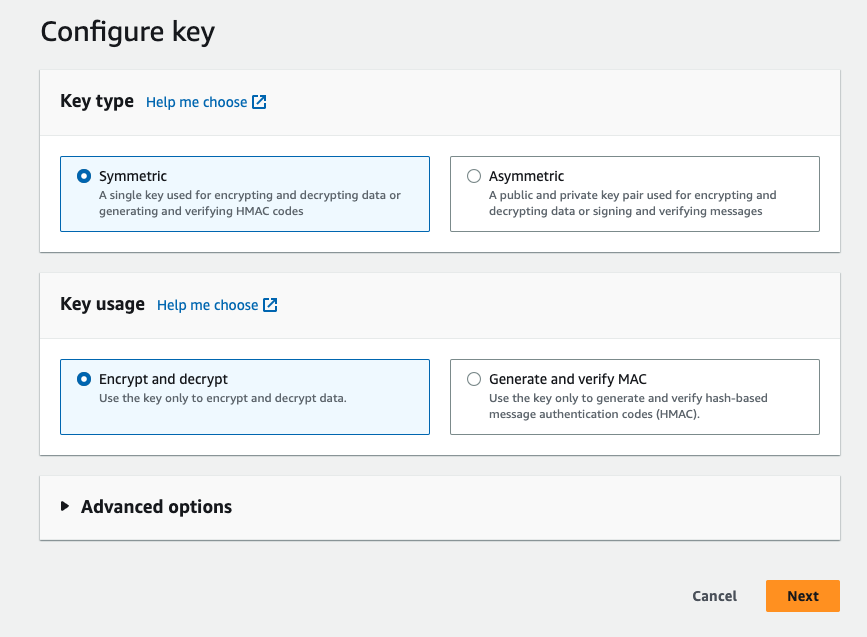
<li>Under <strong>Key type</strong>, choose <strong>Symmetric</strong>. Under <strong>Key usage</strong>, select <strong>Encrypt and decrypt</strong>.</li>
</ol>

<blockquote class="warning">
  <div class="tip-quote">
    
    <div class="tip-text">S3 supports only <a href="https://docs.aws.amazon.com/kms/latest/developerguide/concepts.html#symmetric-cmks" >symmetric CMKs</a>.</div>
  </div>
</blockquote>

<figure class="image--main "  >
    <a 
         href="/docs/images/event-stream-destinations/aws-kms-3.webp"
        
        >
        <img src="/docs/images/event-stream-destinations/aws-kms-3.webp" 
         alt="Key type and usage"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

<ol start="4">
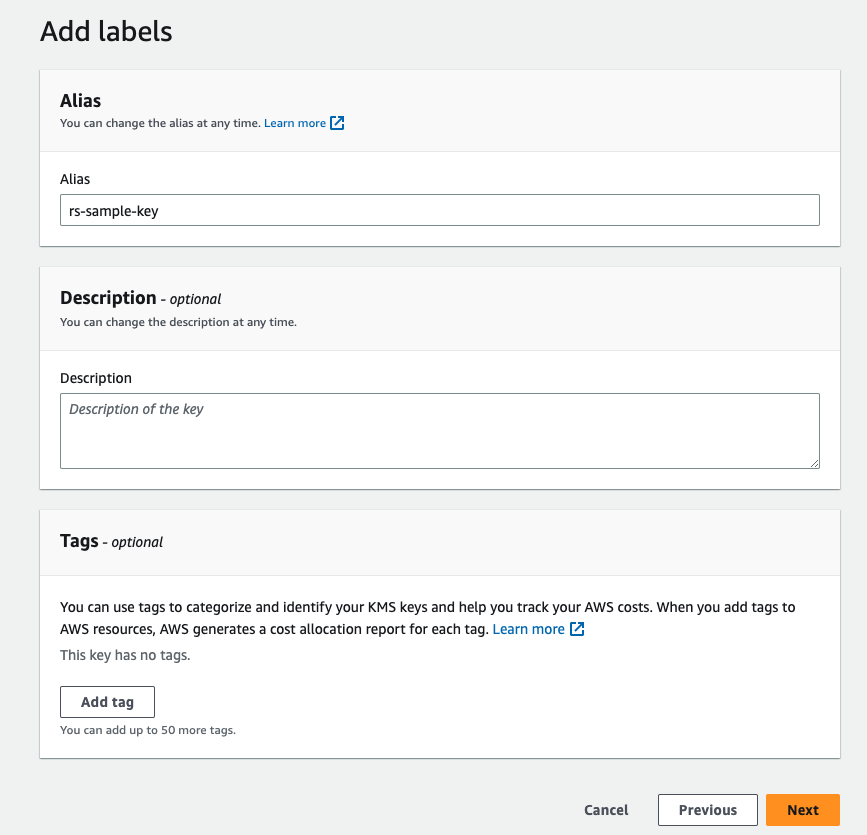
<li>Set an <strong>Alias</strong> for the key. You can also add a description or tags for the key as required.</li>
</ol>

<figure class="image--main "  >
    <a 
         href="/docs/images/event-stream-destinations/aws-kms-4.webp"
        
        >
        <img src="/docs/images/event-stream-destinations/aws-kms-4.webp" 
         alt="Key alias and description"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

<ol start="5">
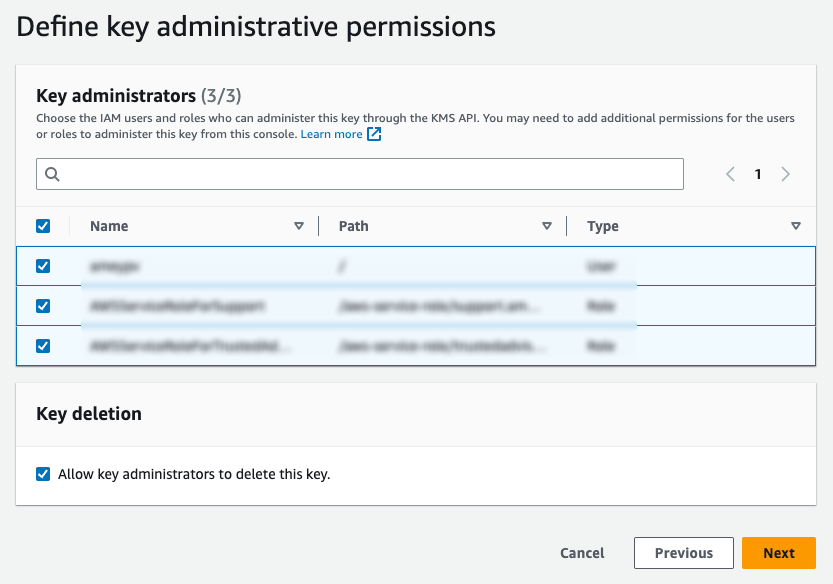
<li>Choose the IAM user or role who can administer and use this key.</li>
</ol>

<figure class="image--main "  >
    <a 
         href="/docs/images/event-stream-destinations/aws-kms-5.webp"
        
        >
        <img src="/docs/images/event-stream-destinations/aws-kms-5.webp" 
         alt="Key adminstration and usage"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

<ol start="6">
<li>Review the configuration and click <strong>Finish</strong> to create the customer managed key.</li>
<li>Finally, <a href="#set-default-encryption" >set the default encryption</a> for your S3 bucket as <strong>AWS KMS-managed keys (SSE-KMS)</strong> and select this customer managed key.</li>
</ol>
<!-- end-chunk -->
<!-- begin-chunk -->
<h3 id="s3-managed-keys">S3 managed keys</h3><p>When you enable the <strong>Enable Server Side Encryption</strong> dashboard setting while configuring your S3 destination, RudderStack adds a <code>x-amz-server-side-encryption</code> header with the value <code>AES256</code> to all the <code>PutObject</code> requests. S3 then encrypts the object with the AES256 encryption algorithm. For more information, see <a href="https://docs.aws.amazon.com/AmazonS3/latest/dev/SSEUsingRESTAPI.html" >S3 encryption with S3 managed keys</a>.</p>

<blockquote class="warning">
  <div class="tip-quote">
    
    <div class="tip-text">If you <a href="#set-default-encryption" >set the default encryption</a> key type to <strong>Amazon S3 managed keys (SSE-S3)</strong>, then S3 encrypts the objects that are uploaded in the bucket with AES256 encryption - irrespective of whether the <strong>Enable Server Side Encryption</strong> is enabled in the RudderStack dashboard or the presence of the <code>x-amz-server-side-encryption</code> header in the <code>PutObject</code> requests.</div>
  </div>
</blockquote>
<!-- end-chunk -->
<!-- begin-chunk -->
<h2 id="where-rudderstack-stores-the-data">Where RudderStack stores the data</h2><p>RudderStack stores the data in the S3 bucket in the following format:</p>
<p><code>rudder-logs/sourceId/date/timestamp.sourceID.uuid.json.gz</code></p>
<p>In this case:</p>
<ul>
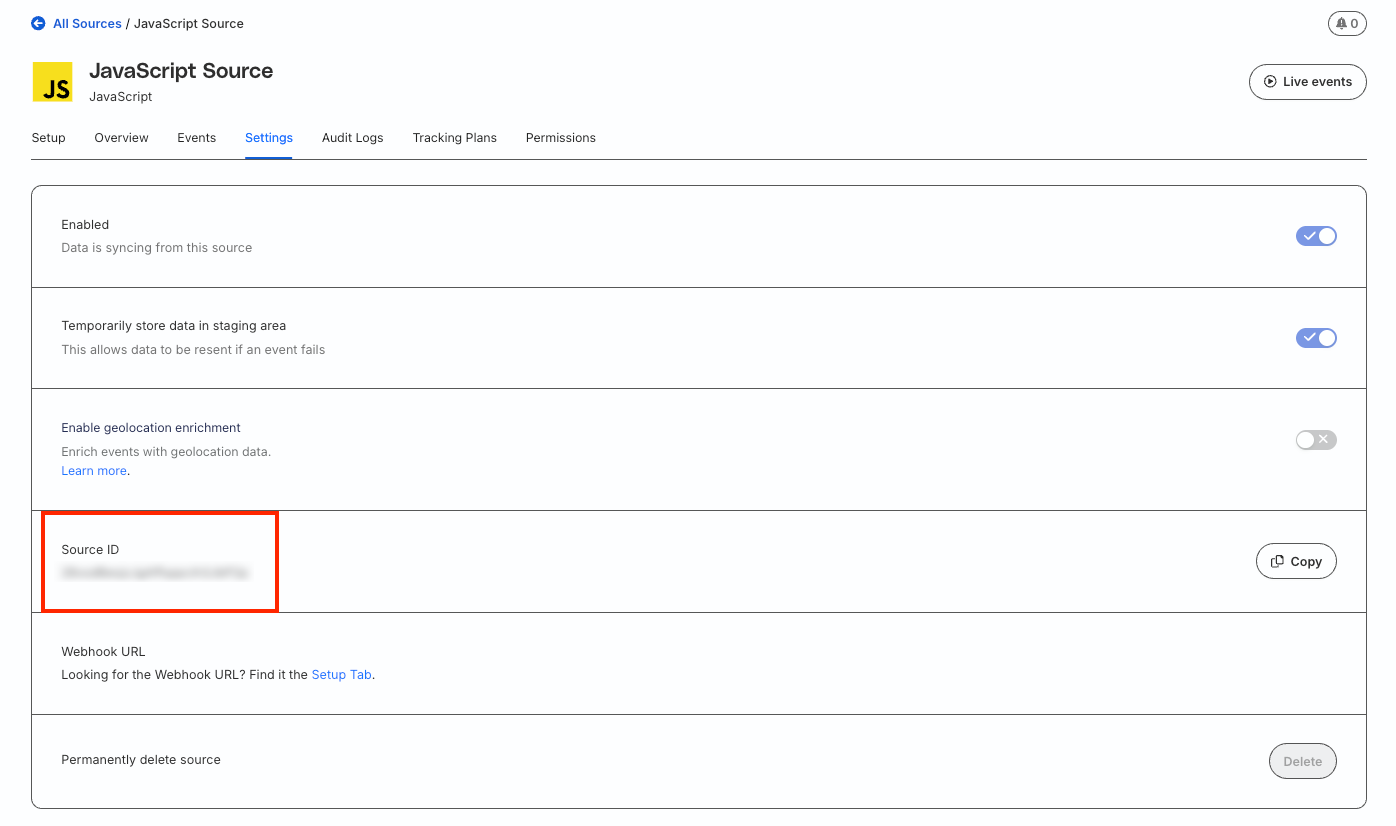
<li><code>sourceId</code> corresponds to the source ID in the RudderStack dashboard. You can find it by going to the <strong>Settings</strong> tab within your source:</li>
</ul>

<figure class="image--main "  >
    <a 
         href="/docs/images/event-stream-sources/sourceid.webp"
        
        >
        <img src="/docs/images/event-stream-sources/sourceid.webp" 
         alt="Source ID in RudderStack dashboard"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

<ul>
<li><code>date</code> corresponds to the upload date.</li>
<li><code>timestamp</code> corresponds to upload timestamp.</li>
</ul>

<html lang="en">
<blockquote class="info">
  <div class="tip-quote">
    
    <div class="tip-text"><p>Note that the events within the file might not correspond to the same upload date.</p>
<p>For example, events from January 1, 2025 at 23:59 hrs might go into the next day&rsquo;s file if the upload happens on that day, for example, on January 2, 2025 at 00:02 hrs.</p>
</div>
  </div>
</blockquote>

</html>
<!-- end-chunk -->
<!-- begin-chunk -->
<h3 id="delete-a-user">Delete a user</h3><p>You can delete a user in S3 using the <a href="https://www.rudderstack.com/docs/api/user-suppression-api/#adding-a-suppression-with-delete-regulation" >Suppression with Delete regulation</a> of the RudderStack <a href="https://www.rudderstack.com/docs/api/user-suppression-api/" >User Suppression API</a>.</p>

<blockquote class="warning">
  <div class="tip-quote">
    
    <div class="tip-text">While RudderStack forwards the deletion request, it <strong>does not guarantee</strong> deletion within a 30-day window. You will need to check with Amazon S3 if the request is fulfilled.</div>
  </div>
</blockquote>
<p>To delete a user, specify the <code>userId</code> in the event.A sample regulation request body for deleting a user in S3 is shown below:</p>
<div class="rs-code">
  <div class="rs-code__head">json<button class="rs-code__copy" type="button">
      
      Copy
    </button>
  </div>
  <div class="highlight"><pre class="chroma"><code class="language-json" data-lang="json">{
  &#34;regulationType&#34;: &#34;suppress_with_delete&#34;,
  &#34;destinationIds&#34;: [&#34;2FIKkByqn37FhzczP23eZmURciA&#34;],
  &#34;users&#34;: [
    {
      &#34;userId&#34;: &#34;1hKOmRA4GRlm&#34;,
      &#34;&lt;customKey&gt;&#34;: &#34;&lt;customValue&gt;&#34;
    }
  ]
}</code></pre></div>
</div>