# Personal Access Tokens


<blockquote class="warning">
  <div class="tip-quote">
    
    <div class="tip-text"><p><strong>Use Personal Access Tokens for development or testing purposes only.</strong></p>
<p>For production use cases, RudderStack recommends using the following over a Personal Access Token:</p>
<ul>
<li><a href="https://www.rudderstack.com/docs/access-management/service-access-tokens/#workspace-level-sats" >Workspace-level Service Access Tokens</a> for working with workspace-level resources and APIs</li>
<li><a href="https://www.rudderstack.com/docs/access-management/service-access-tokens/#organization-level-sats" >Organization-level Service Access Tokens</a> for working with <a href="https://www.rudderstack.com/docs/user-guides/sso-setup/" >SSO SCIM</a>, the <a href="https://www.rudderstack.com/docs/api/audit-logs-api/" >Audit Log API</a>, and the <a href="https://www.rudderstack.com/docs/api/organization-usage-api/" >Organization Usage API</a>.</li>
</ul>
</div>
  </div>
</blockquote>
<p>This guide explains the concept of <strong>Personal Access Tokens</strong> in RudderStack&rsquo;s Access Management system. It also describes the steps to generate a Personal Access Token and all the operations associated with it.</p>
<!-- end-chunk -->
<!-- begin-chunk -->
<h2 id="overview">Overview</h2><p>To consume the public RudderStack APIs, you need a <strong>Personal Access Token</strong> (PAT). This access token is associated with an individual&rsquo;s RudderStack account.</p>
<!-- end-chunk -->
<!-- begin-chunk -->
<h3 id="permissions">Permissions</h3><p>You can create and use Personal Access Tokens with the following scopes:</p>
<table>
  <thead>
      <tr>
          <th>Token scope</th>
          <th><div>Description</div></th>
      </tr>
  </thead>
  <tbody>
      <tr>
          <td>Read-Only</td>
          <td>Access tokens will have read-only permissions.</td>
      </tr>
      <tr>
          <td>Read-Write</td>
          <td>Access tokens will have both read-only and read-write permissions of the user. <br /><br />
<html lang="en">
<blockquote class="info">
  <div class="tip-quote">
    
    <div class="tip-text">If a user having read-only permissions creates a <strong>Read-Write</strong> token, then the token will still have read-only permissions.</div>
  </div>
</blockquote>

</html></td>
      </tr>
      <tr>
          <td>Admin</td>
          <td>
<blockquote class="warning">
  <div class="tip-quote">
    
    <div class="tip-text">Creation of new Personal Access Tokens with Admin scope is deprecated. However, any existing Admin PATs will continue to work as before, even after migration.</div>
  </div>
</blockquote></td>
      </tr>
  </tbody>
</table>
<!-- end-chunk -->
<!-- begin-chunk -->
<h2 id="personal-access-tokens-vs-service-access-tokens">Personal Access Tokens vs. Service Access Tokens</h2><table>
  <thead>
      <tr>
          <th>Personal Access Tokens (PAT)</th>
          <th>Service Access Tokens (SAT)</th>
      </tr>
  </thead>
  <tbody>
      <tr>
          <td>Tied to a specific user within a workspace.</td>
          <td>Not tied to an individual user.</td>
      </tr>
      <tr>
          <td>Used for individual tasks and testing.</td>
          <td>Used for centralized, shared access and production use cases.</td>
      </tr>
      <tr>
          <td>Any processes dependent on these tokens will break if the user is removed from the organization or a breaking change is made to their permissions.</td>
          <td>Exist at an organization or workspace level, ensuring continuity in essential workflows and pipelines using these tokens.</td>
      </tr>
  </tbody>
</table>
<!-- end-chunk -->
<!-- begin-chunk -->
<h2 id="generate-personal-access-token">Generate Personal Access Token</h2><ol>
<li>Log in to your <a href="https://app.rudderstack.com/" >RudderStack dashboard</a>.</li>
<li>Go to <strong>Settings</strong> &gt; <strong>Your Profile</strong> and scroll down to <strong>Personal Access Tokens</strong>. Then, click <strong>Generate new token</strong>:</li>
</ol>

<figure class="image--main "  >
    <a 
         href="/docs/images/rudderstack-api/personal-access-token.webp"
        
        >
        <img src="/docs/images/rudderstack-api/personal-access-token.webp" 
         alt="New Personal Access Token in RudderStack dashboard"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

<ol start="3">
<li>Enter the <strong>Token name</strong>, select the <strong>Workspace</strong> and the <strong>Scope</strong> from the respective dropdowns:</li>
</ol>

<figure class="image--main "  >
    <a 
         href="/docs/images/rudderstack-api/personal-access-token-scope.webp"
        
        >
        <img src="/docs/images/rudderstack-api/personal-access-token-scope.webp" 
         alt="Personal Access Token name and scope"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

<ol start="4">
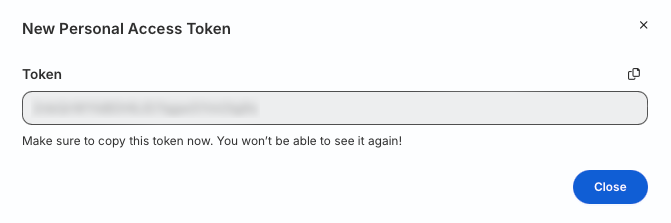
<li>Click <strong>Generate</strong>.</li>
<li>Note the Personal Access Token value.</li>
</ol>

<blockquote class="warning">
  <div class="tip-quote">
    
    <div class="tip-text">Make sure to secure the generated token — the token value is not visible again once you close this window.</div>
  </div>
</blockquote>

<figure class="image--main "  >
    <a 
         href="/docs/images/rudderstack-api/personal-access-token-3.webp"
        
        >
        <img src="/docs/images/rudderstack-api/personal-access-token-3.webp" 
         alt="Personal Access Token details"  
         
         
        decoding="async" loading="lazy" class="img-shortcode"/>
    </a>
    
</figure>

<!-- end-chunk -->
<!-- begin-chunk -->
<h2 id="delete-personal-access-token">Delete Personal Access Token</h2><ol>
<li>Go to <strong>Settings</strong> &gt; <strong>Your Profile</strong> and scroll down to <strong>Personal Access Tokens</strong>.</li>
<li>Click the <strong>Delete</strong> option next to the token and confirm by clicking <strong>Yes, delete</strong>.</li>
</ol>
<!-- end-chunk -->
<!-- begin-chunk -->
<h2 id="migrate-old-personal-access-tokens">Migrate old Personal Access Tokens</h2><p>After migration, Personal Access Tokens:</p>
<ul>
<li><strong>Inherit user permissions</strong>: Personal Access Tokens continue to inherit the permissions of the user who created them. Since user permissions are migrated to their <a href="https://www.rudderstack.com/docs/access-management/members/" >Member Workspace Policy</a>, Personal Access Tokens automatically reflect those permissions.</li>
<li><strong>Maintain scope behavior</strong>: Personal Access Tokens created with <strong>Read-Only</strong> or <strong>Read-Write</strong> scopes continue to work as before, with their effective permissions determined by the user&rsquo;s <a href="https://www.rudderstack.com/docs/access-management/members/" >Individual Workspace Policy</a>.</li>
</ul>
<p>See the <a href="https://www.rudderstack.com/docs/access-management/migration-examples/personal-access-tokens/" >Migration Scenarios</a> guide for detailed examples of how Personal Access Tokens are migrated to the new Access Management system.</p>
<br />